Personalized Outbound Strategy
Get The Right Outbound Strategy In Minutes
Enter your email to get a custom plan & stack recommendation for your business
It's being carefully crafted by AI
Please check your mailbox in 5 minutes
Open your sending domain’s DNS settings, and you’ll see three lines of text starting with v=spf1, v=DKIM1, and v=DMARC1. If a provider set up your domains, you may never have read them. That’s fine until one stops working.
Here’s why they’re easy to overlook. These records rarely fail when you first set them up. They fail later, when someone adds a second SPF record for a new tool, overwrites the wrong entry during a bulk DNS update, or leaves DKIM signing with Google’s key instead of yours. Nothing seems broken. Your emails just start landing in spam, and you look for problems in your copy or list.
So even if your provider handles setup, it helps to know what each record checks and how to spot a broken one.
Together, these three records form the core of SMTP authentication, the checks a prospect’s mail server runs before trusting your email. I’ll explain how SPF, DKIM, and DMARC work, how to set them up across several cold email domains, and how to spot a broken record before it affects your campaigns.
Copy these, and replace yourdomain.com with your own domain:
When your email reaches a prospect’s mail server, the server doesn’t simply trust the sender. It checks. SPF, DKIM, and DMARC are the three records it checks, and together they determine whether it treats your email as genuine.
One note on the term. Your sending tool also logs into your mailbox, and that login is sometimes called SMTP authentication too. This guide covers the checks at the receiving end.
Each record answers a different question for the receiving server.
Each record fills a gap the others leave, which is why a cold email domain needs all three. If your domains come from Mailforge, Infraforge, or Primeforge, they’re already set up. Your job is to keep them working.
SPF and DKIM each check something separately. DMARC connects those checks to the address your prospect sees.
Cold email usually runs across several secondary domains, not your main one. Each needs its own records in its own DNS. A missing or broken record on one domain can hurt your results, even when everything else is set up correctly.
Gmail and Yahoo’s rules also set a minimum standard. Since February 2024, both require bulk senders—those sending 5,000 or more emails daily to their users—to use SPF, DKIM, and DMARC and keep spam complaints below 0.3%. Every sender, regardless of volume, needs at least SPF or DKIM.
You might think the bulk sender rules don’t apply because you mostly email business addresses. Gmail’s 5,000-email count covers only personal accounts, so Workspace addresses don’t count.
But that’s a reason to stay below the threshold, not to skip records. Microsoft began enforcing DMARC for Outlook in May 2025, and having all three records means your domain passes each provider’s checks without you having to track which rules apply.
SPF, short for Sender Policy Framework, lists the servers allowed to send email for your domain. You publish it as a TXT record in your domain’s DNS. When an email arrives, the receiving server checks that list to see whether the server that sent it is allowed.
A record starts with v=spf1, lists who can send, and ends with a rule for everyone else. Here’s a simple one for a domain using Google Workspace.
v=spf1 include:_spf.google.com ~allThe include part points the check to Google’s list of mail servers, so you don’t have to track their IP addresses. A domain sending from one dedicated IP can list that address directly. Infraforge’s DNS screen shows this kind of record, built around a single IP4 entry.
Cold email senders often ask whether they should add their sending tool to SPF. Usually not. If your tool sends through a Google or Microsoft mailbox, the email still leaves from their servers, and those are what SPF checks. Add a service only if it sends from its own servers using your domain.
The ending tells receiving servers how to handle mail from a server outside your list.
The major providers differ here. Google’s instructions use ~all, while Microsoft’s use -all. Once DMARC is in place, receiving servers use its policy to decide what to do anyway.
So I’d follow your mailbox provider’s recommendation and use DMARC to tighten the rules.
SPF allows up to 10 DNS lookups per check. Each include counts, along with any includes nested inside it. Go over 10, and the check fails. A domain can also have only one SPF record. Two records mean a broken setup, not a combined one.
To see what your record holds right now, look up your domain in Salesforge’s free SPF Record Checker.
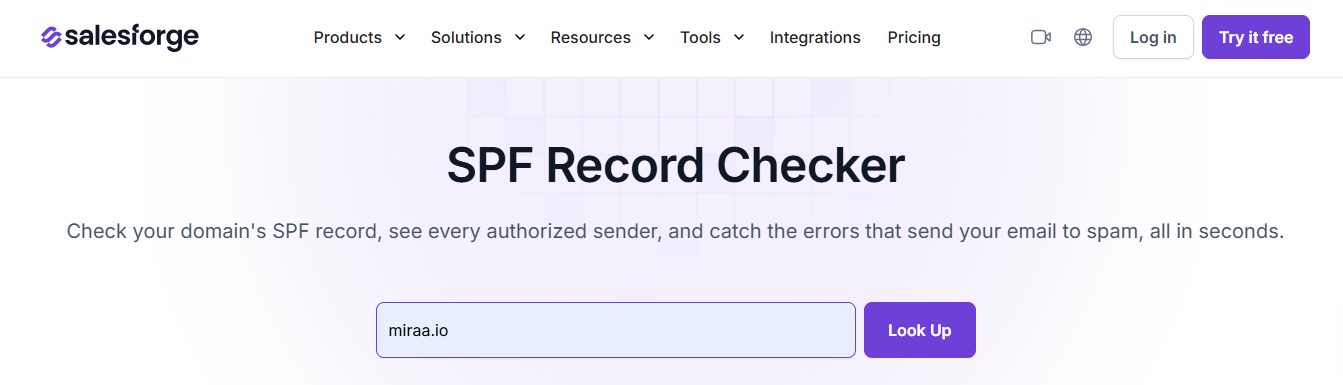
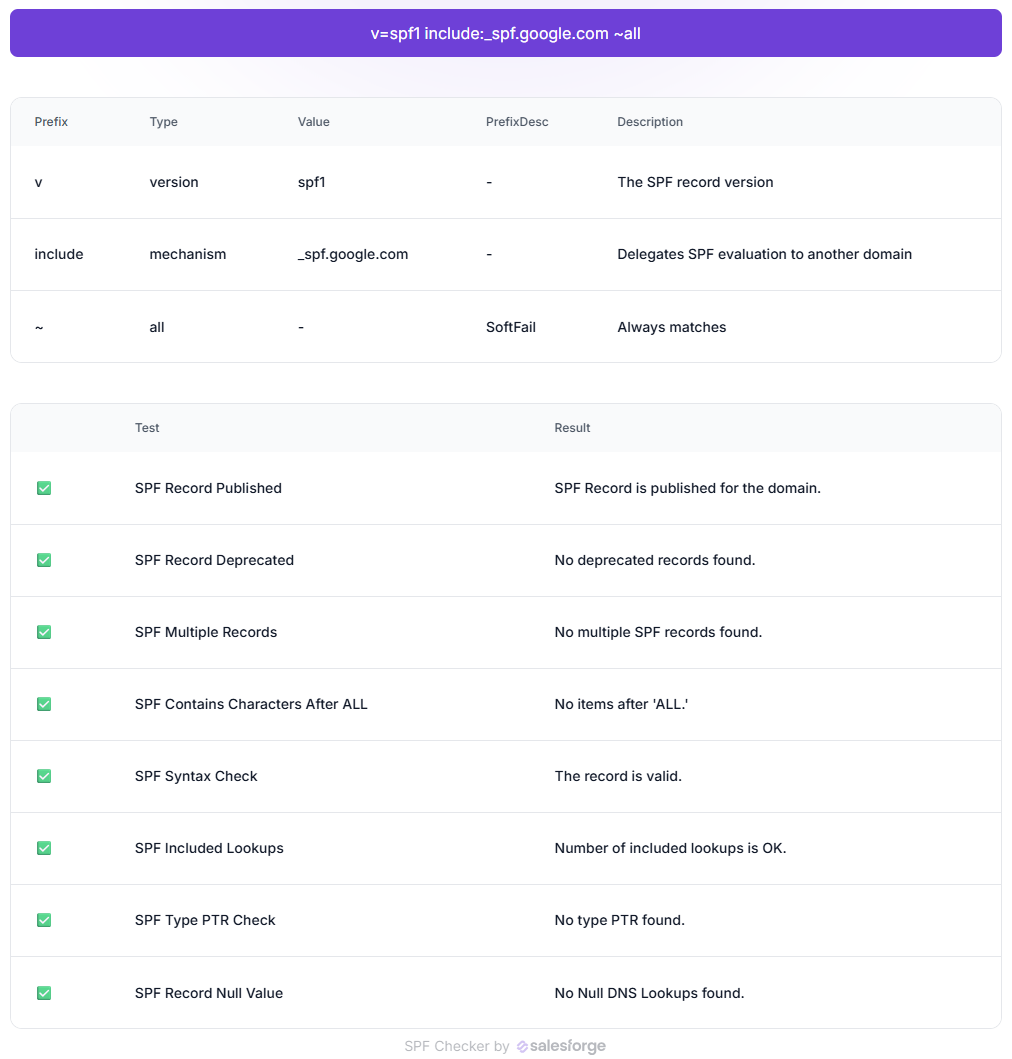
It lists every sender your record allows and points out errors that can send your mail to spam.
Secondary domains used only for cold email rarely reach this limit because they send through one provider. That’s another reason to keep them separate from your main domain, where every marketing and support tool needs its own include.
Forwarding is SPF’s weak spot. A forwarded email arrives from someone else’s server, which isn’t on your list. DKIM covers that gap.
DKIM adds a signature to every email you send. Your mail server signs each message with a private key only it holds. The matching public key sits in your DNS, where receiving servers can find it and check the signature.
If the signature passes, the receiver knows the email came from a server your domain trusts, and nobody changed it along the way.
The public key lives in a TXT record named something like default._domainkey.yourdomain.com. The first part, default in this example, is the selector. This label lets a domain publish several keys, so you can add a new one without breaking the old one.
Aim for a 2048-bit key. You can recognize one in DNS by its opening characters, as a 2048-bit public key starts with p=MIIBIjANBgkq. Infraforge’s DNS screen shows a record like this.
v=DKIM1; h=sha256; k=rsa; p=MIIBIjANBgkq...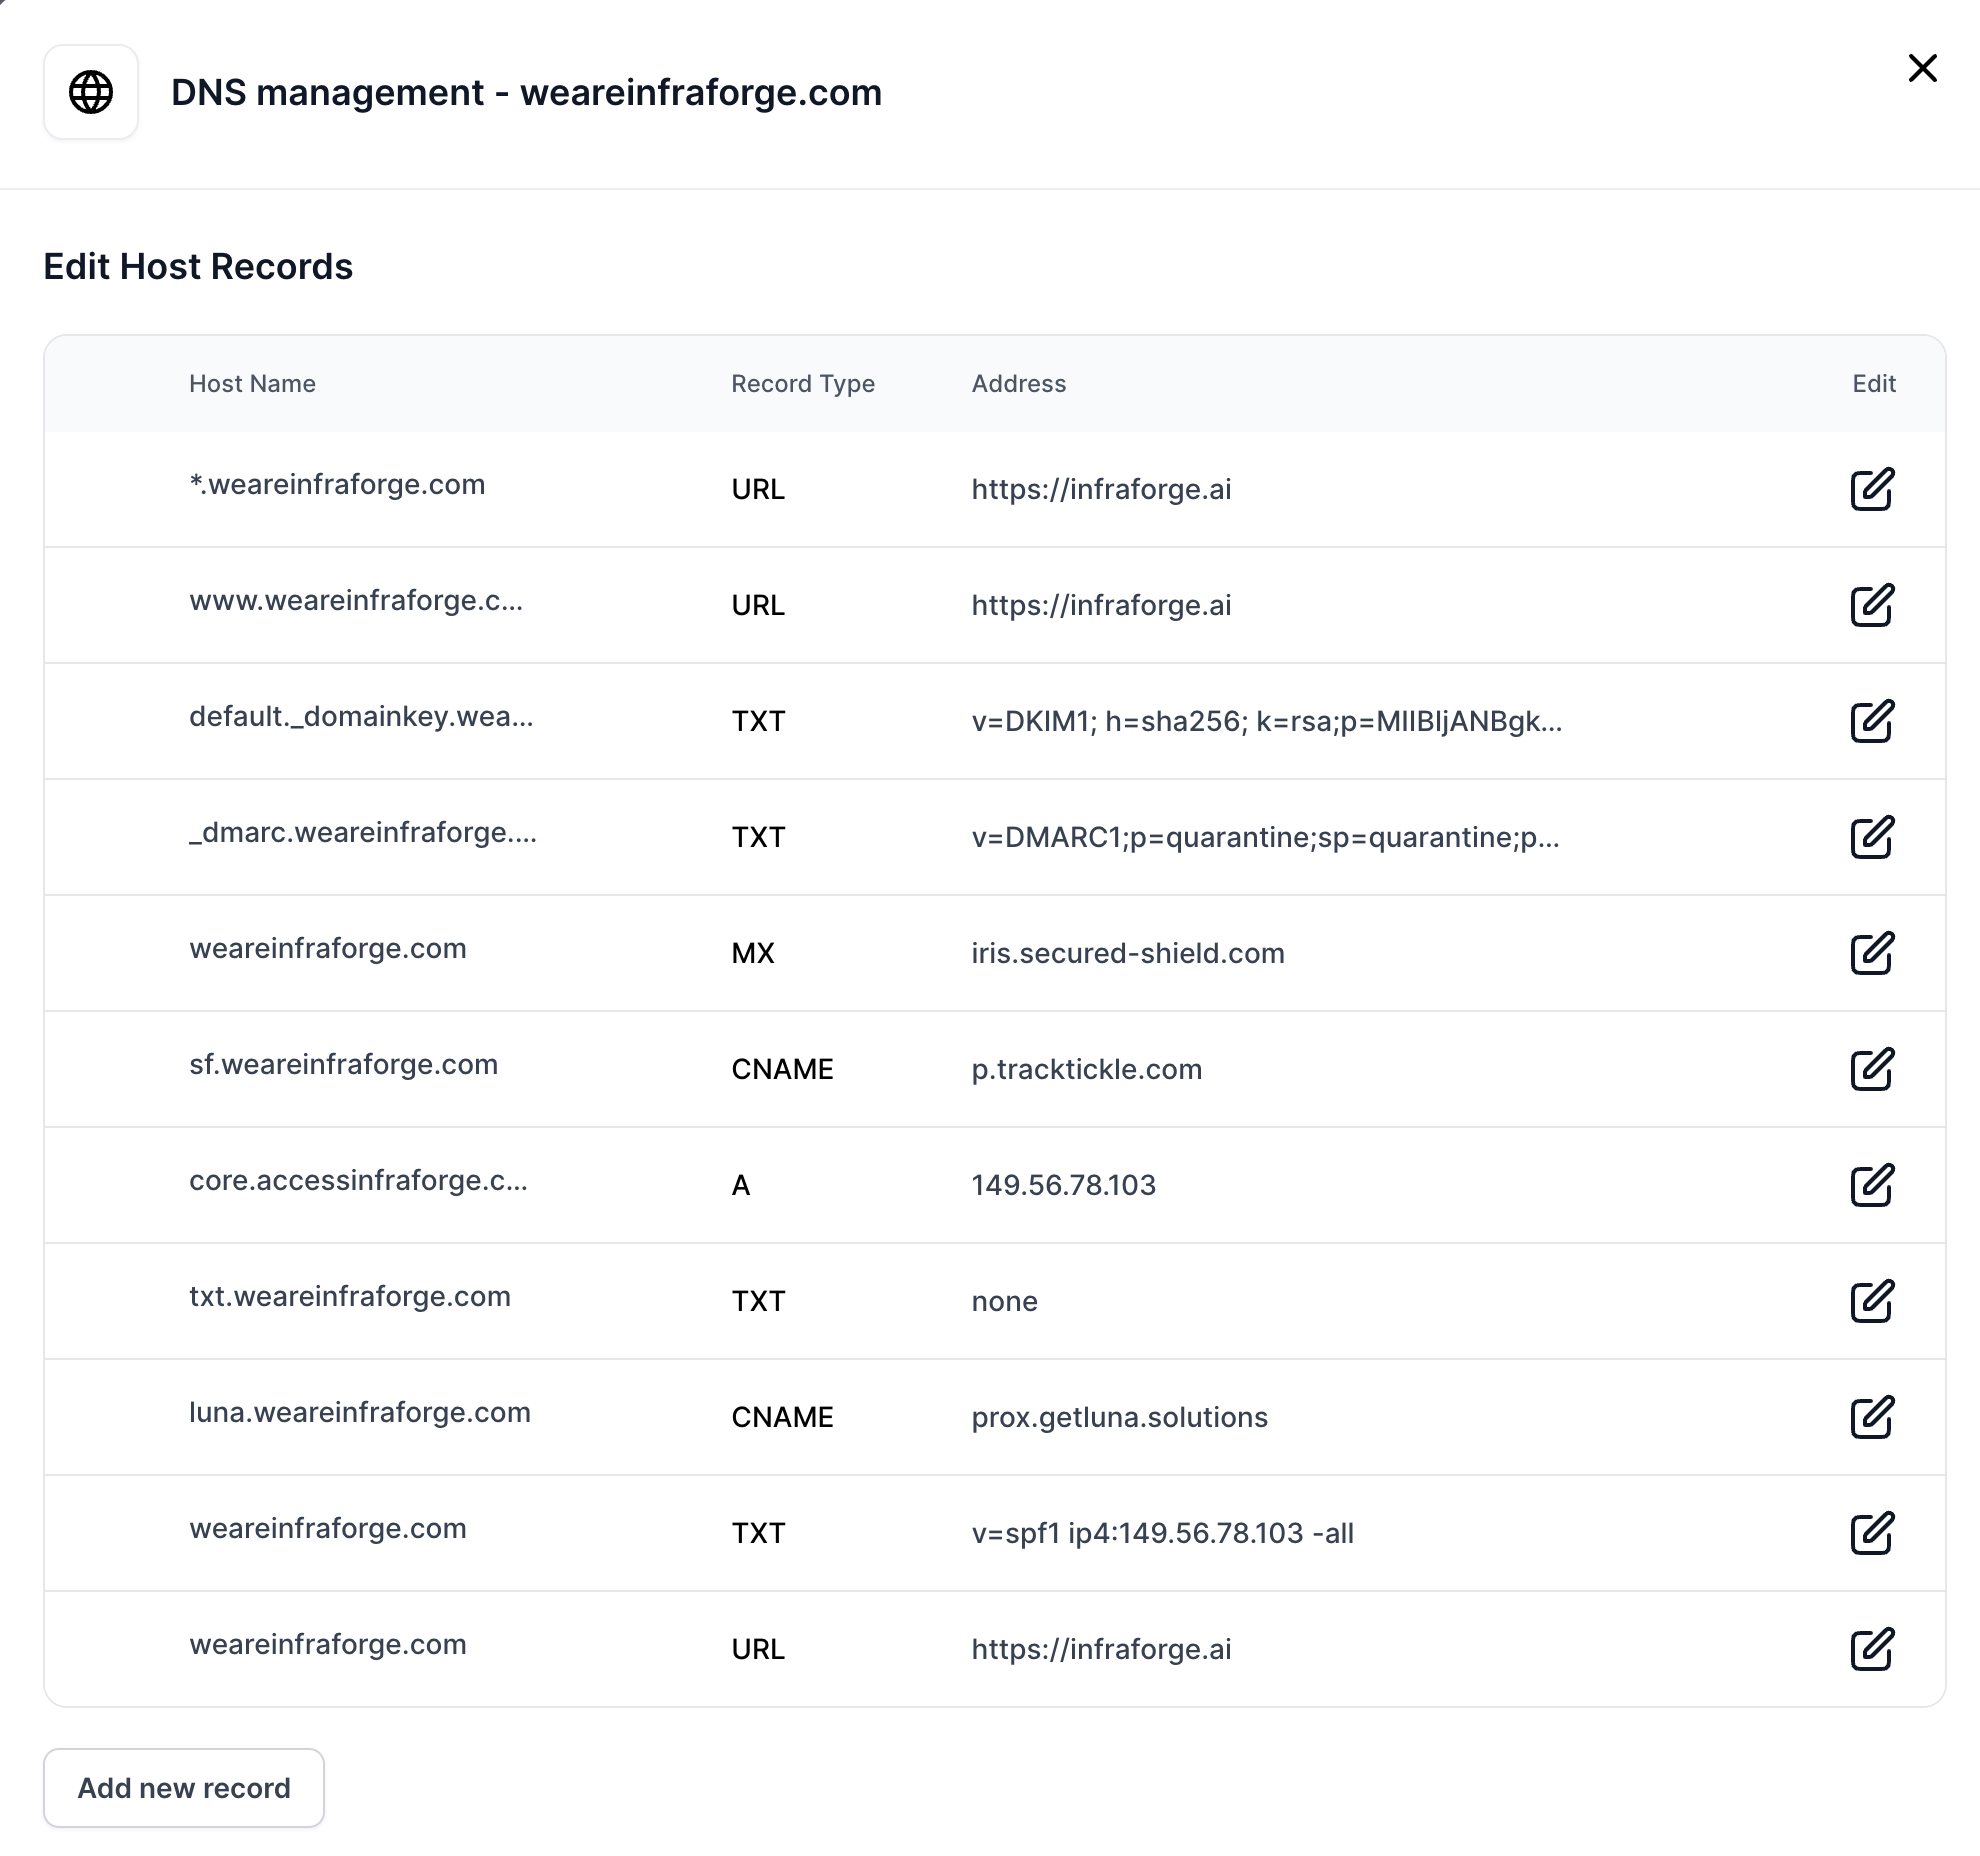
One detail trips up many cold email senders. Google Workspace and Microsoft 365 sign mail with a default key even without DKIM setup, but that key belongs to their domain, not yours.
Your emails pass DKIM, but the signature doesn’t match your From address, so it doesn’t help DMARC. A matching signature requires DKIM setup for your own domain.
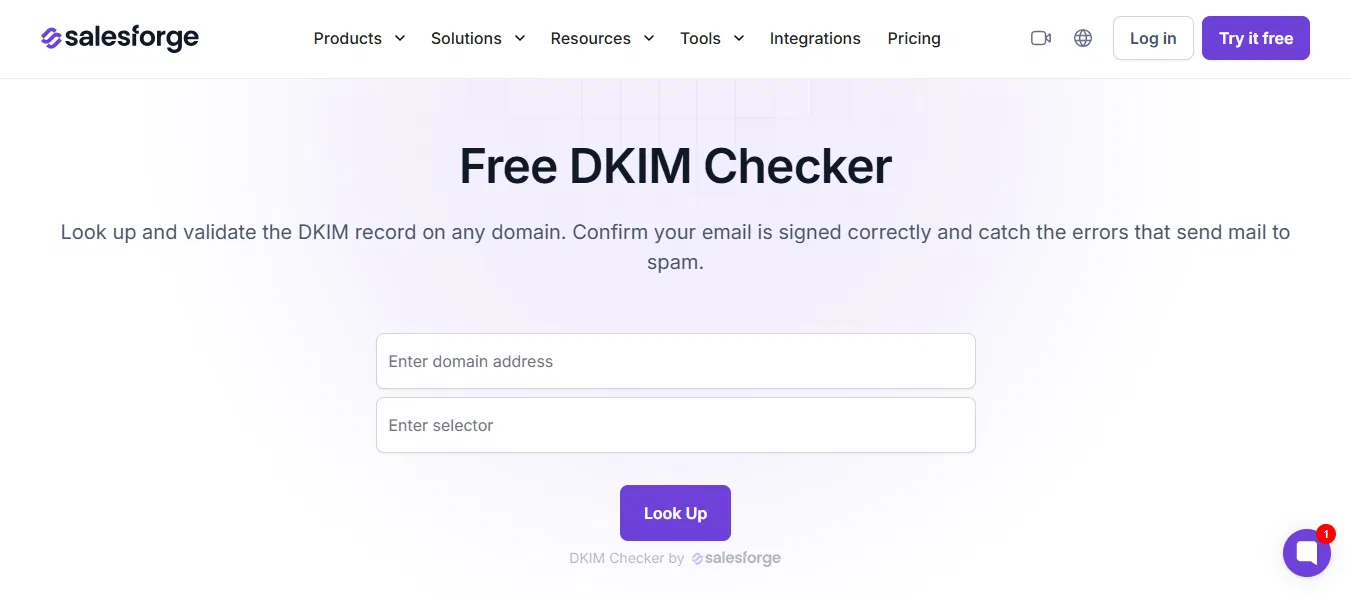
To confirm your own key is published, enter your domain and selector in the free Salesforge DKIM Checker. The selector is google for Google Workspace, and selector1 or selector2 for Microsoft 365.
If your provider manages DKIM, it handles the keys. If you manage them, rotate them regularly and immediately if a private key may have been exposed.
Publish the new key under a new selector, switch signing to it, and leave the old public key in DNS for a while so receivers can still check emails signed with it.
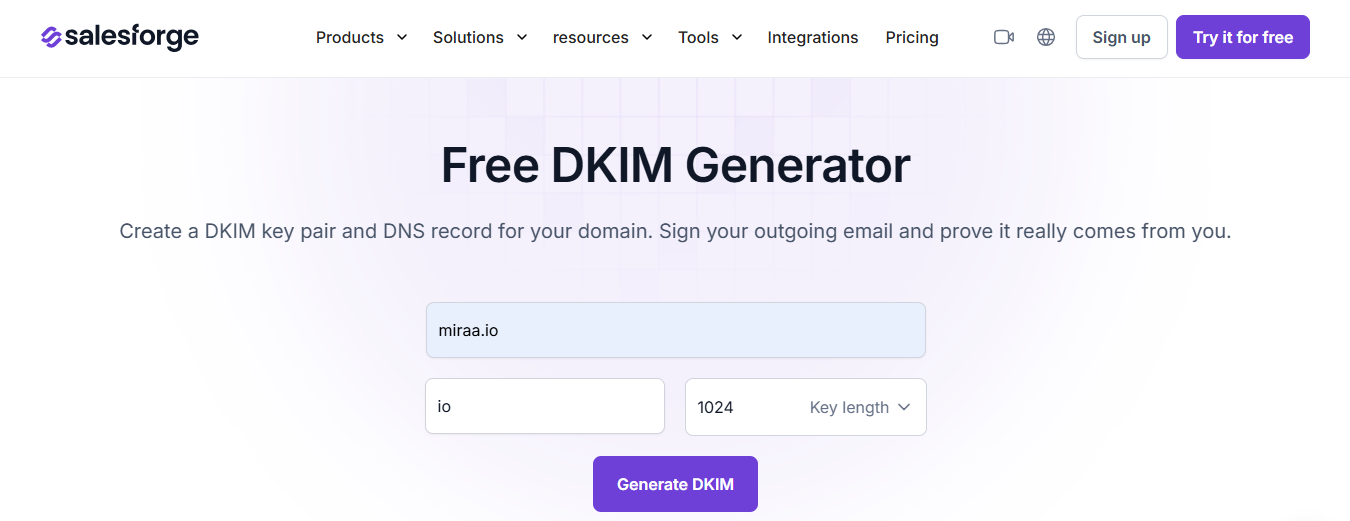
“If you need a new key pair, the Salesforge free DKIM Generator creates one, along with the DNS record for the selector you enter. Set the key length to 2048 first, since the tool starts at 1024.
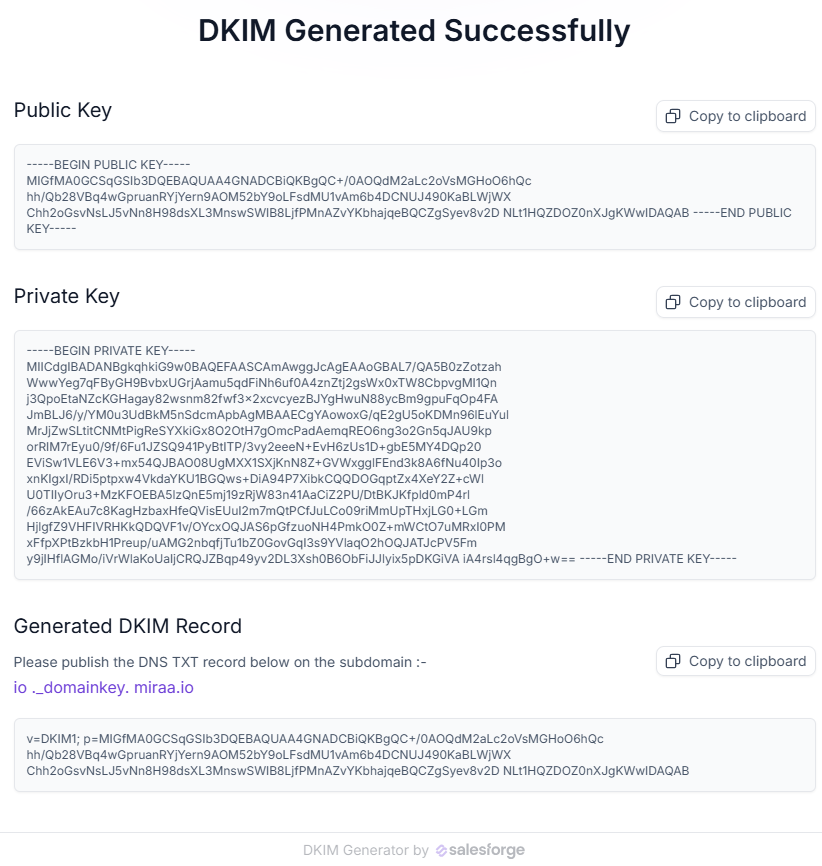
Load the private key onto your mail server, and publish the public key as the TXT record.
DMARC does two jobs. It checks whether your From domain matches a domain that passed SPF or DKIM. And it tells receiving servers how to handle failing mail and where to send reports.
The record is a TXT entry at _dmarc.yourdomain.com. Here’s the one Infraforge creates for a domain.
v=DMARC1; p=quarantine; sp=quarantine; ...The policy protects your domain from people pretending to send as you. It doesn’t affect your mail as long as it passes.
DMARC passes when either condition is true.
SPF checks the hidden Return-Path domain, not the From address your prospect sees. So SPF can pass while DMARC fails if the Return-Path uses a different domain.
"Relaxed" alignment, the default, accepts a subdomain of your From domain. "Strict" alignment requires an exact match.
The rua tag names the address that receives daily aggregate reports from receiving servers. Choose it carefully. Mailforge and Infraforge warn that it will receive lots of DMARC email, so I’d use a dedicated inbox or reporting tool, never your main mailbox.
If you set up DMARC yourself, start with p=none, review reports for a few weeks, fix legitimate mail that fails, then move to quarantine and finally reject.
You can set up these records in two ways. The right choice depends on how many domains you manage.
If you buy domains and mailboxes through Mailforge, Infraforge, or Primeforge, SPF, DKIM, DMARC, and custom domain tracking are set up automatically for each domain. With a dozen secondary domains, that saves you writing and checking 36 records by hand.
You can still change them. Bulk DNS updates let you change DMARC report addresses, DMARC policies, domain forwarding, and CNAME records across several domains.
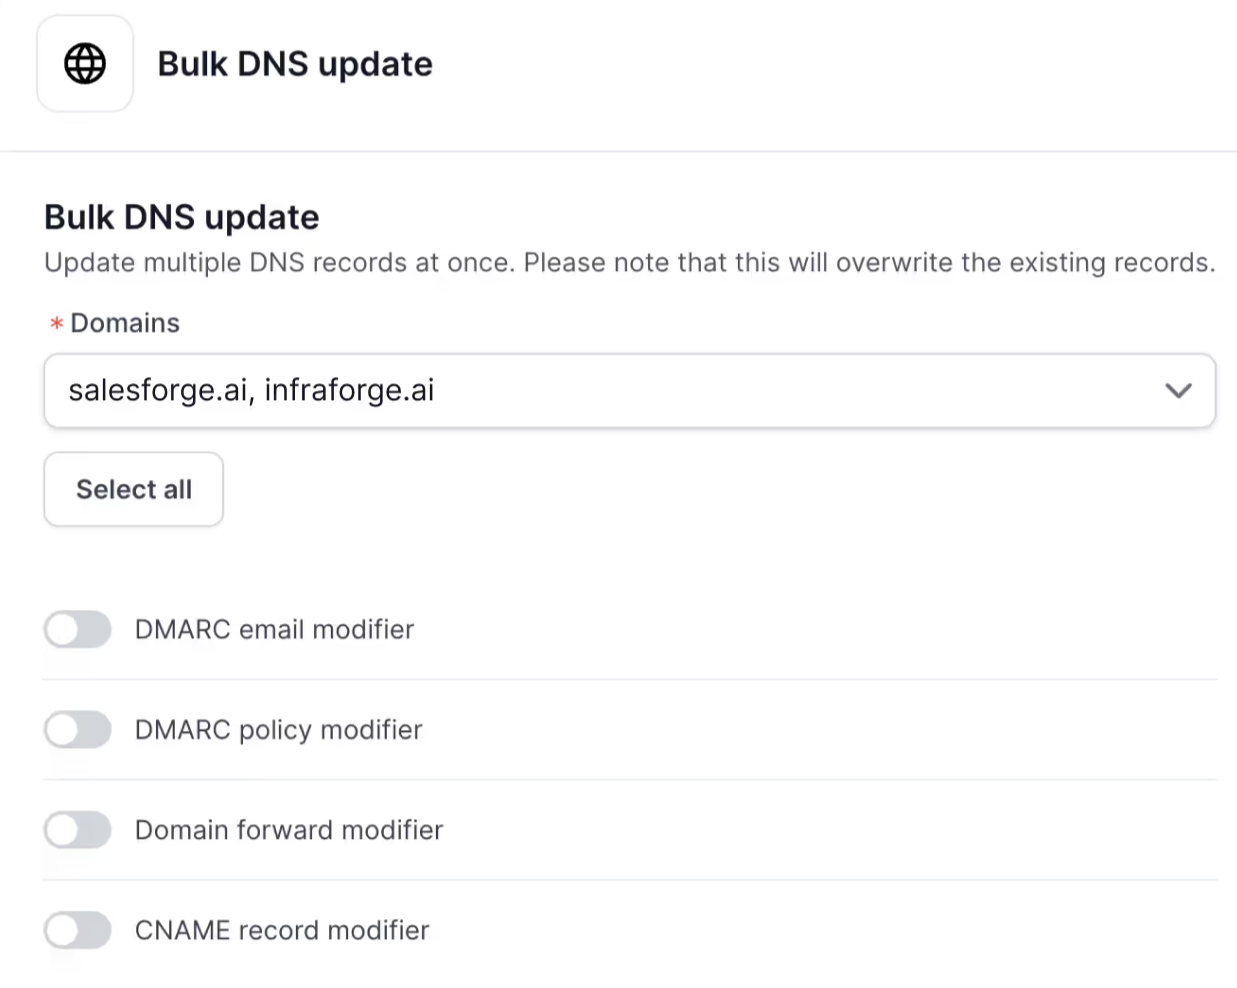
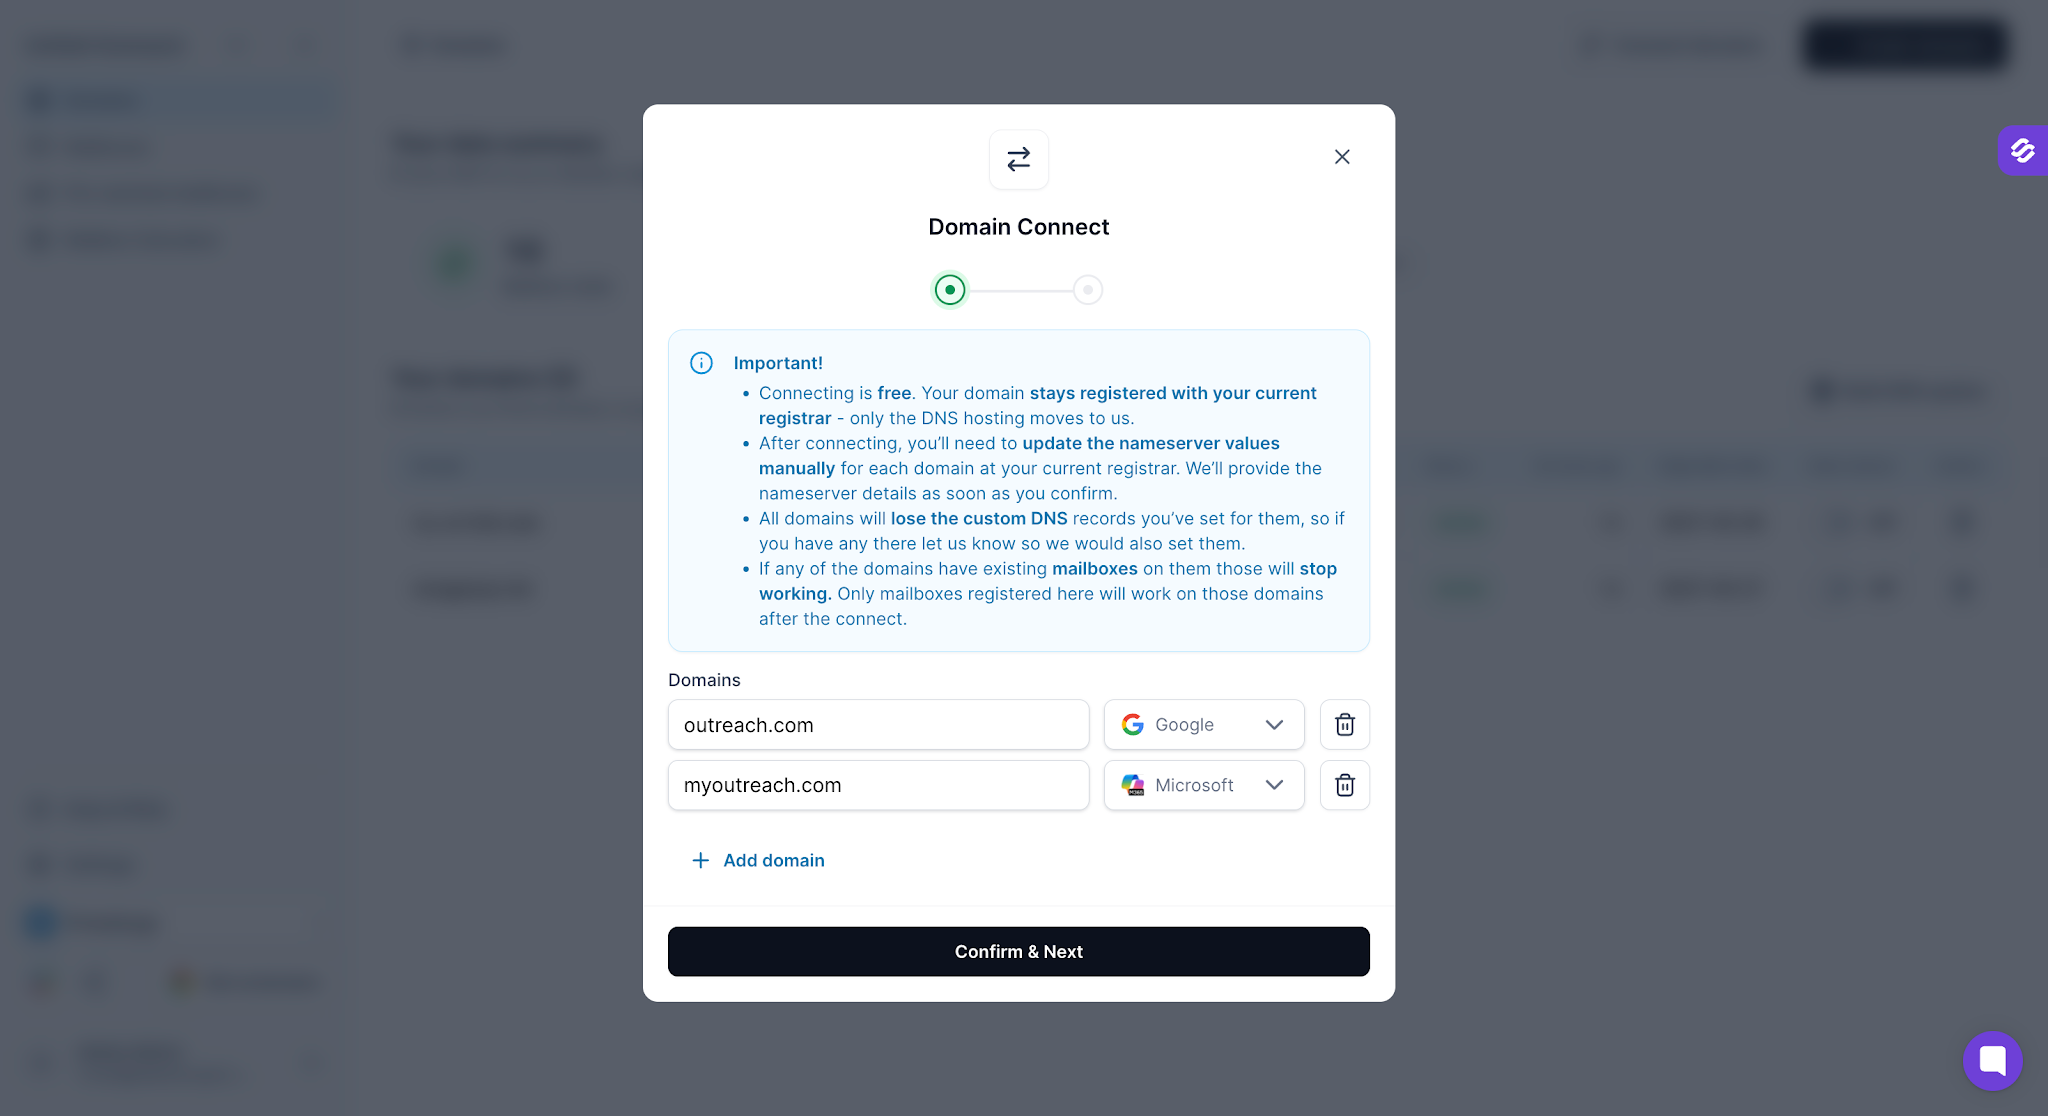
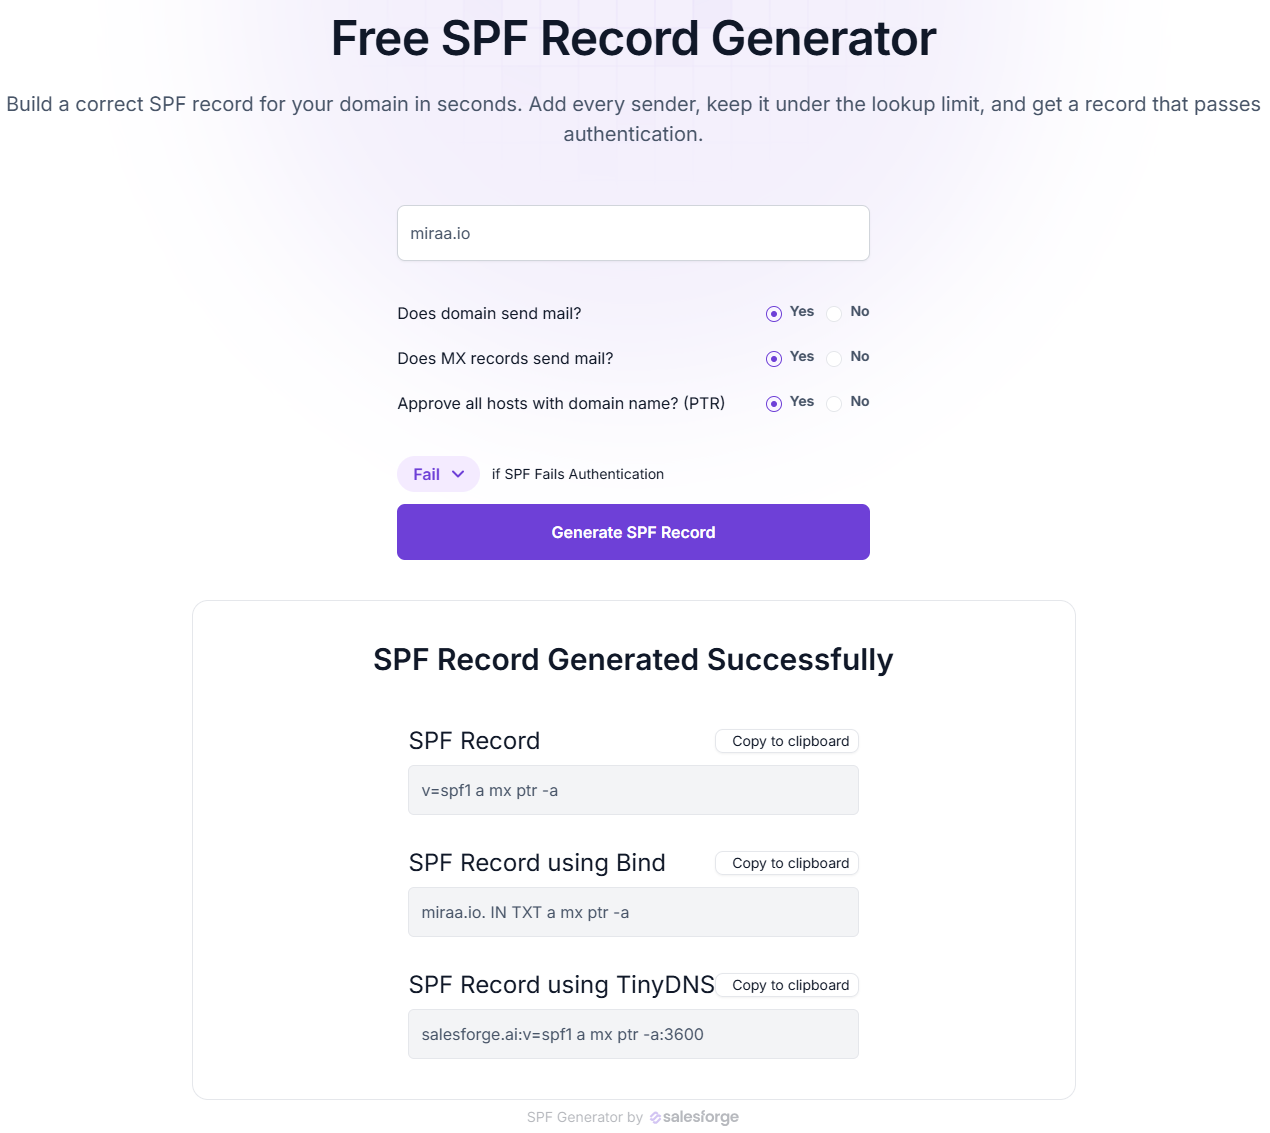
If you manage DNS yourself, follow this order because DMARC depends on the other two.
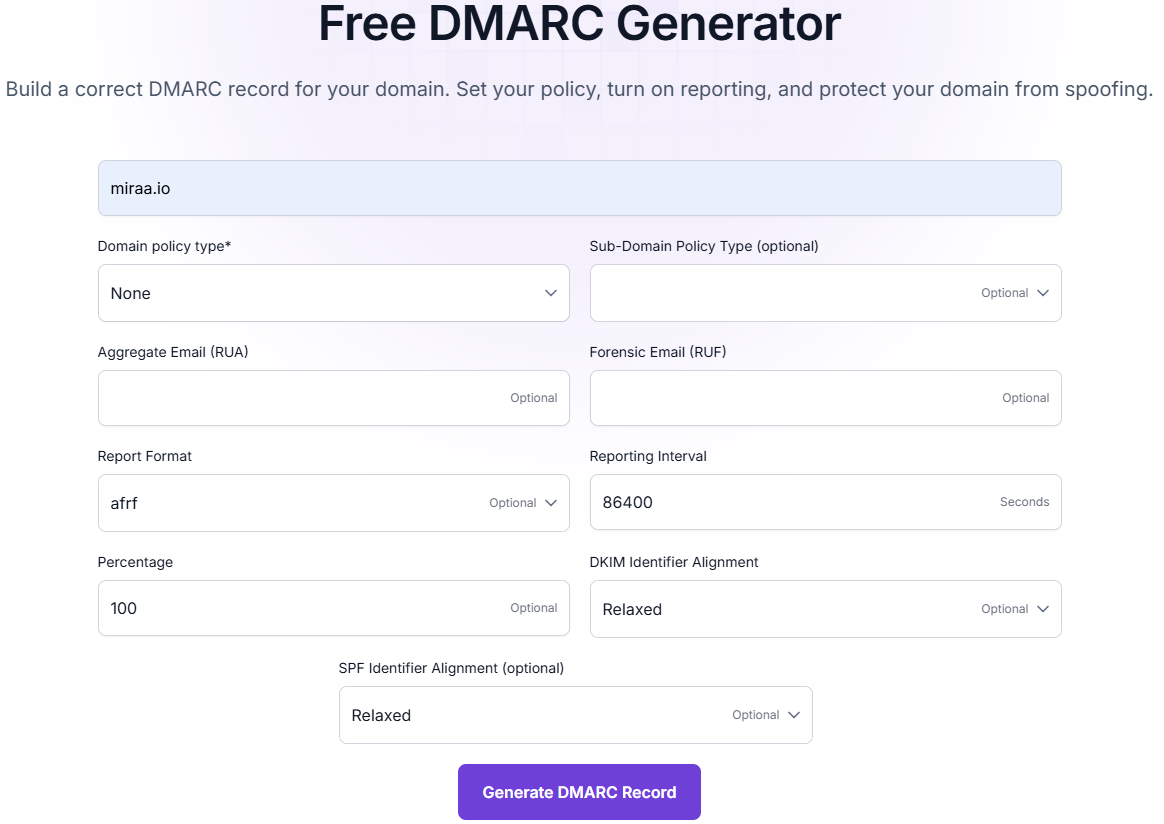
In the Salesforge’s free DMARC Generator, choose None as the policy, add your dedicated report inbox under Aggregate Email (RUA), and leave both alignment settings on Relaxed.
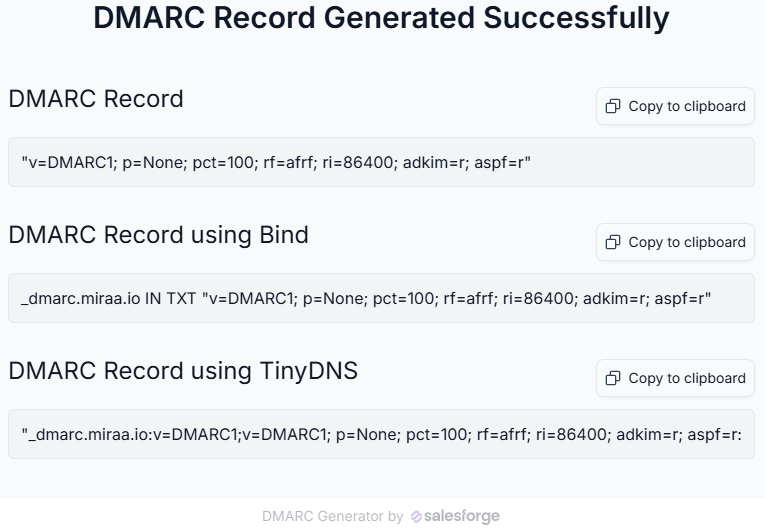
Most failures I see aren’t caused by missing records. The records exist but don’t work properly.
The fifth comes directly from Infraforge’s deliverability guide, which advises against changing existing records or adding conflicting ones.
Even correctly configured records can break later. Someone adds a tool, moves a domain, or overwrites the wrong entry in a bulk update. Here’s how to verify SPF, DKIM, and DMARC records before a break affects your campaigns.
Warmforge’s mailbox list shows SPF, DKIM, and DMARC status for every connected mailbox alongside its heat score and warmup status.
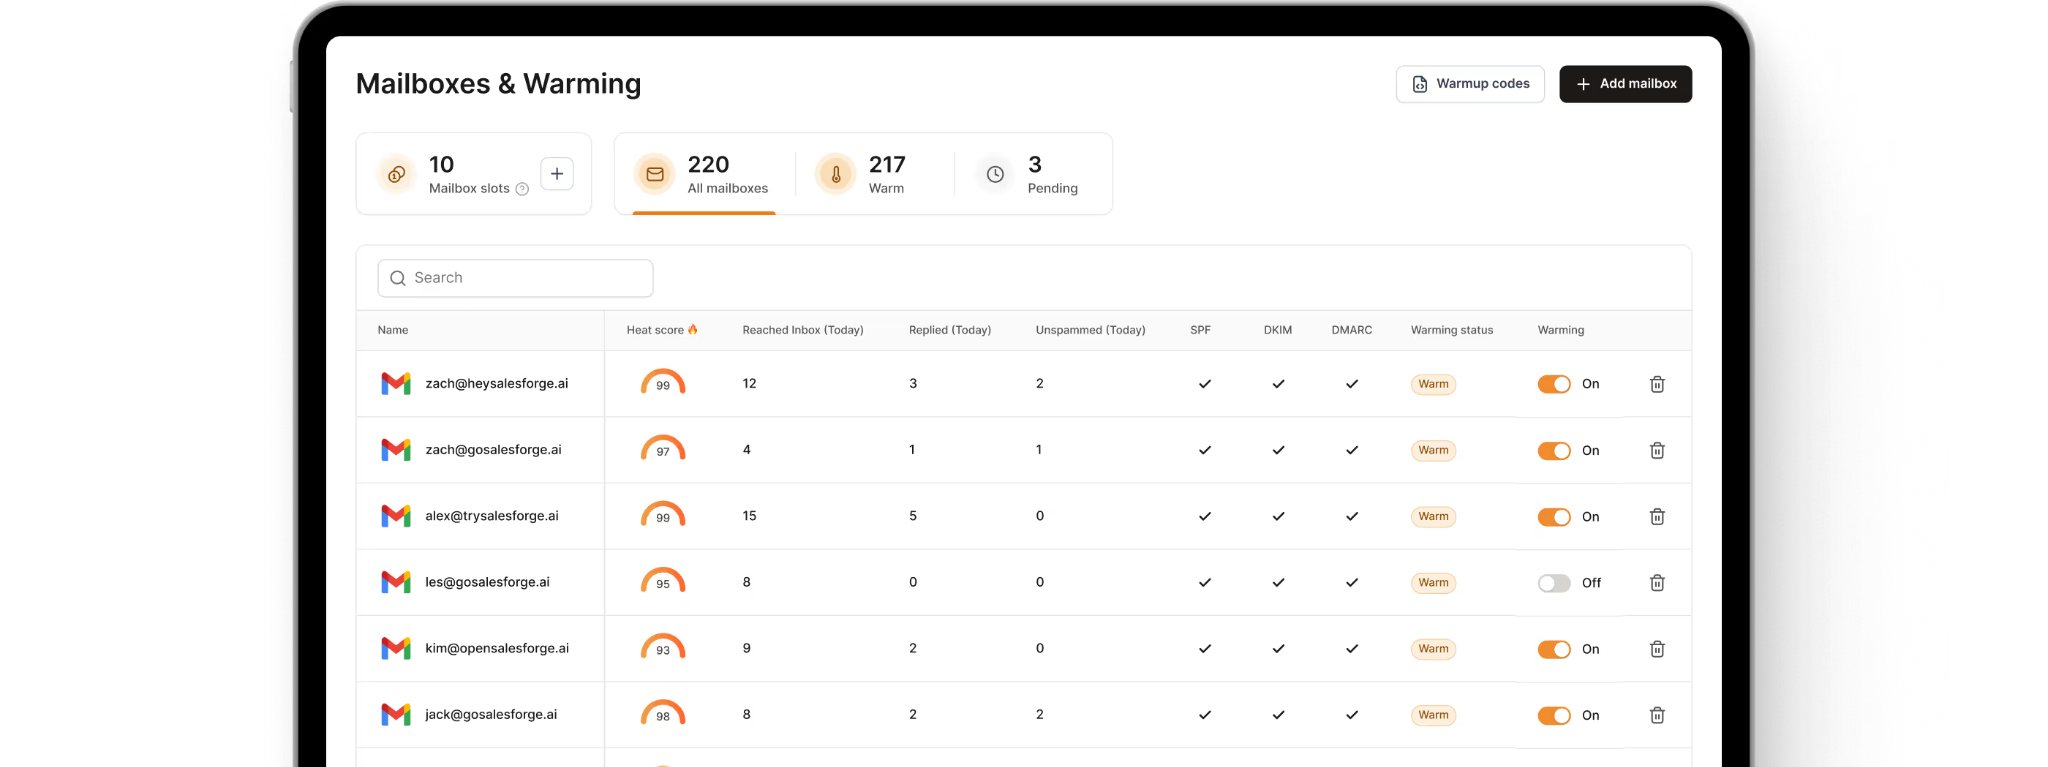
With 30 mailboxes across 10 domains, it’s the quickest way to find the domain with a missing record.
Health checks look more closely at each mailbox. They confirm SPF is present, reverse DNS is configured correctly, and neither your domain nor your server’s IP is blacklisted. They also monitor MX records.
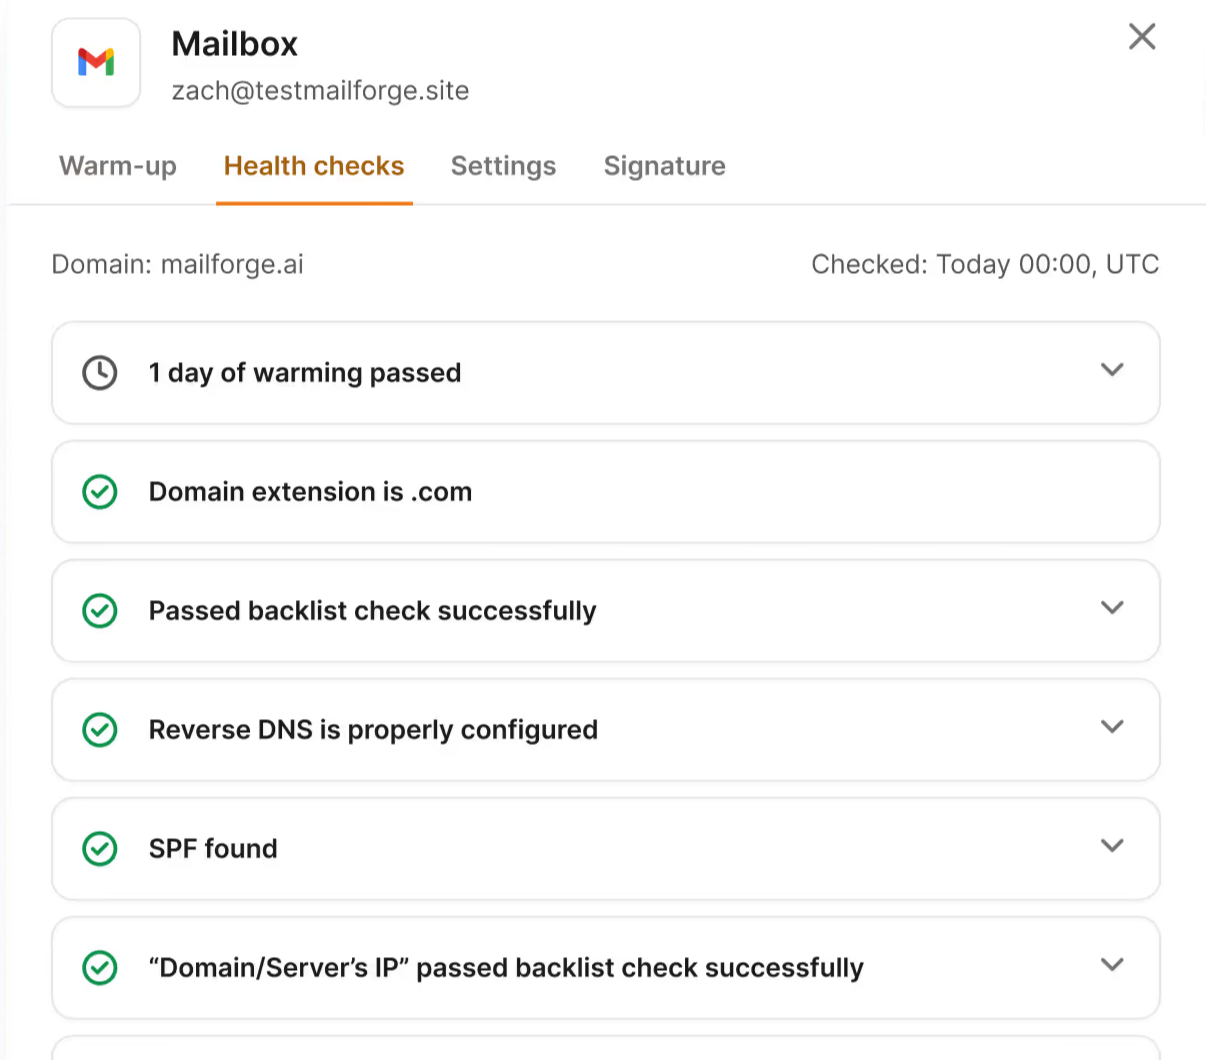
Reverse DNS matters more than you might think. Gmail and Yahoo expect valid forward and reverse DNS for sending IPs, yet people often forget to check it.
Passing authentication checks doesn’t guarantee inbox placement. After changing SPF, DKIM, or DMARC, run a placement test using your actual email copy. It shows how many test emails reached the inbox, landed in spam, or went missing, broken down by Google and Microsoft.
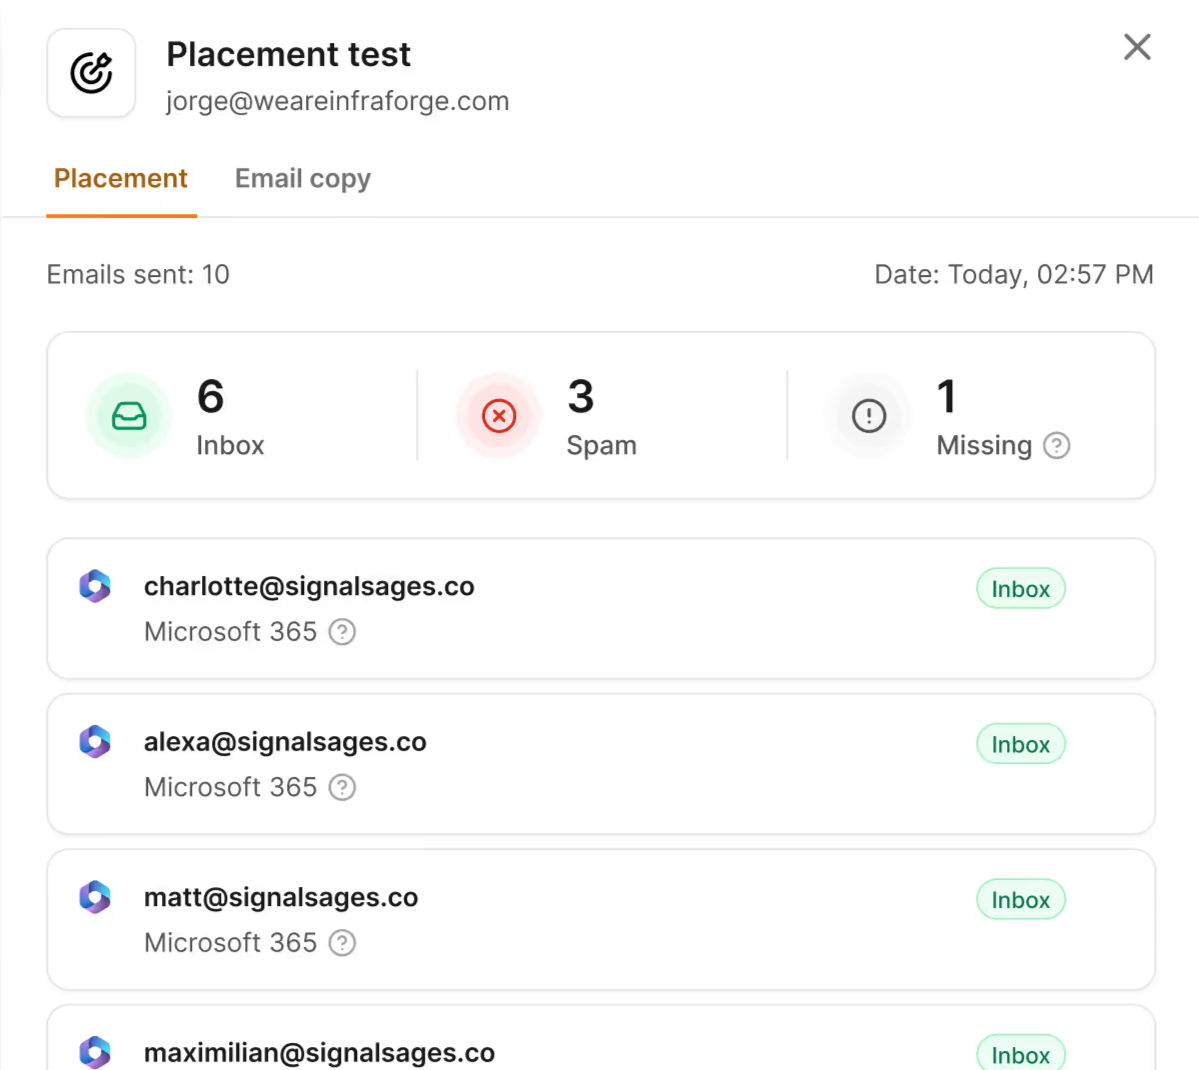
Every Warmforge plan includes one free monthly placement test, and your first Google or Microsoft mailbox slot is free. If you send through Salesforge, Warmforge warmup is included for all your mailboxes.
Enter your email to get a custom plan & stack recommendation for your business
Please check your mailbox in 5 minutes
Send an email from each sending domain to a Gmail address you control. Open it and choose “Show original.” Look for PASS beside SPF, DKIM, and DMARC. If a domain shows FAIL, or DKIM passes under a domain other than yours, fix it before sending anything else.
Then make this a habit. Check again whenever you add a sending tool, move a domain, or run a bulk DNS update.
Warmforge can handle this for you. Connect your mailboxes to see each one’s SPF, DKIM, and DMARC status, with background health checks.
Your first Google or Microsoft mailbox slot is free. If you’re setting up new domains, buying through Mailforge, Infraforge, or Primeforge puts all three records in place from day one.